Sentinel Ops — A SOC
That Triages Itself.
An AI-powered Security Operations Centre platform for enterprise IT. Ingests millions of events per second, correlates them against the MITRE ATT&CK matrix, auto-remediates known patterns, and surfaces only the alerts that need a human. Built for analysts who are tired of drowning.
Why this project existed.
The problem
Modern SOCs ingest 80,000+ events per second across multiple clusters. Analysts see 1,200 alerts a day and can investigate maybe 60. The other 1,140 are noise — but the breach is always somewhere in that pile. Tooling that promised AI triage has historically just added another queue to clear.
The solution
Real-time event ingest with deterministic dedupe and AI-assisted clustering. Each candidate incident is scored against MITRE ATT&CK, attached to its runbook, and auto-remediated when confidence is high. Analysts see a ranked priority queue, a live threat-surface map, and audit-ready runbooks attached to every action.
Built on a deliberate stack.
Every choice in this project was made for two horizons — fast iteration during build, and a 3-5 year operational life with minimal vendor lock-in.
Three views of the system.
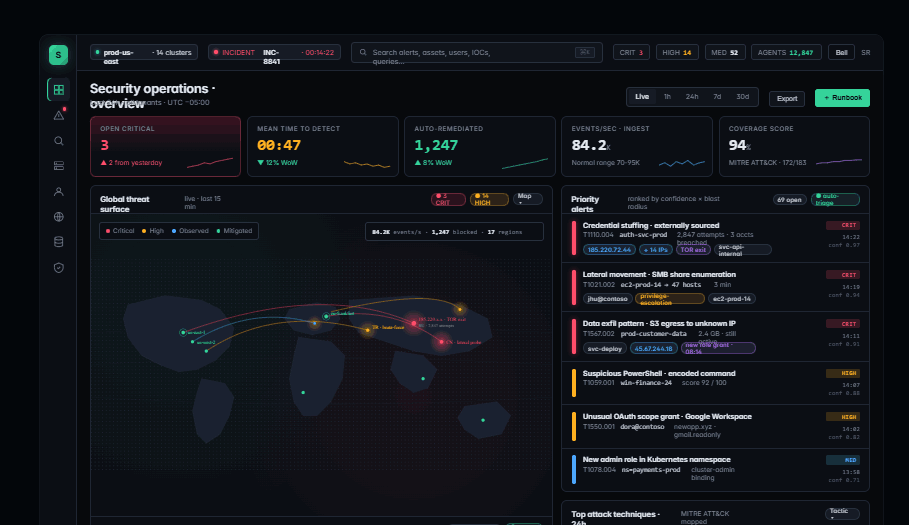
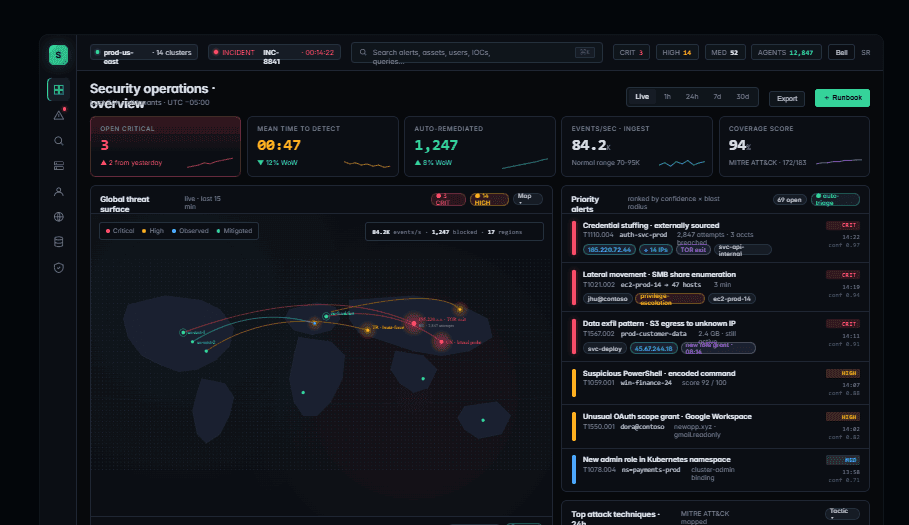
Live threat-surface map, MITRE ATT&CK coverage (172/183), mean time to detect, and a priority alert feed ranked by confidence × blast radius.
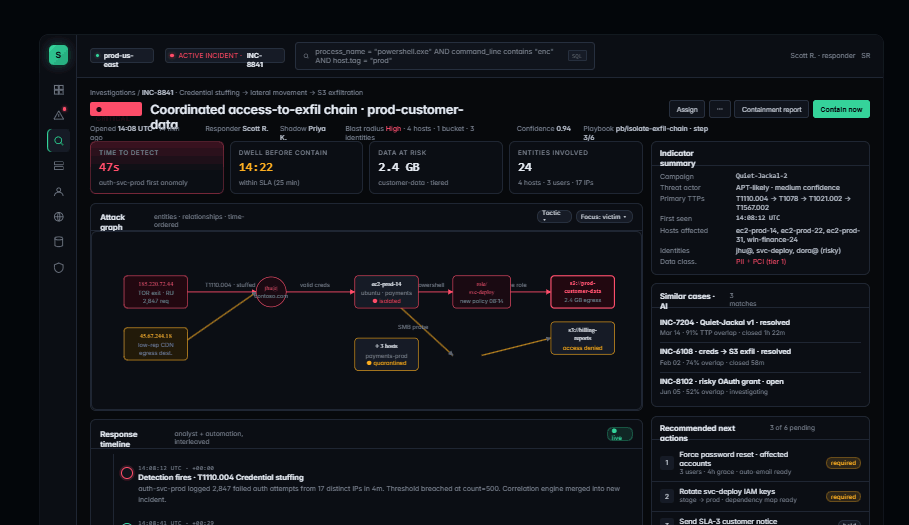
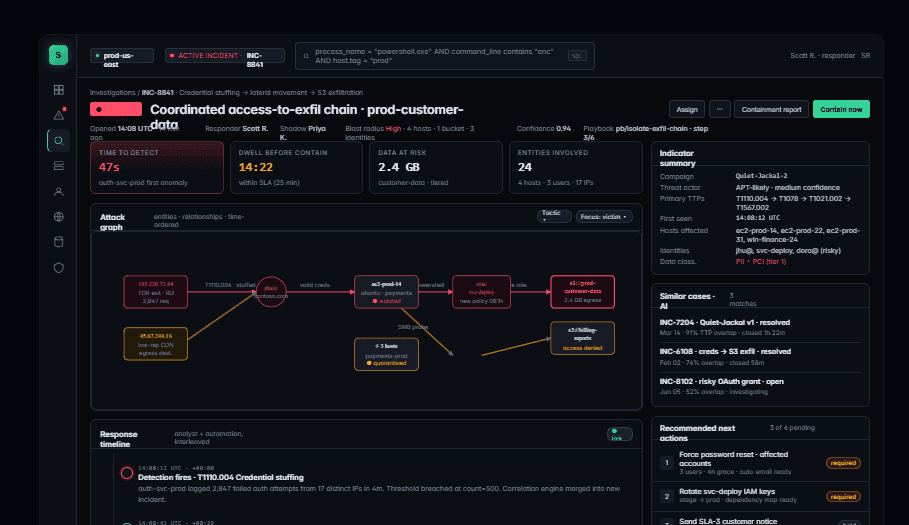
Per-incident timeline with attached runbook, AI-generated narrative summary, related events, and one-click containment actions audited end-to-end.
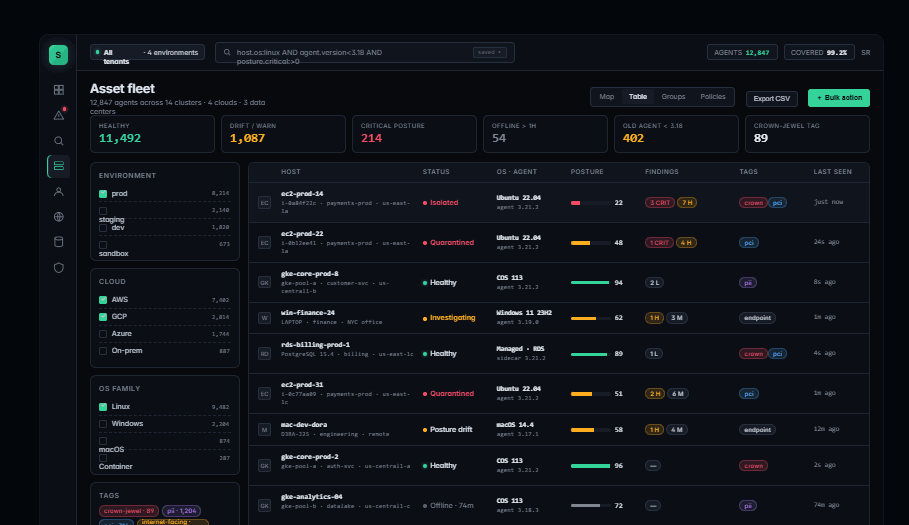
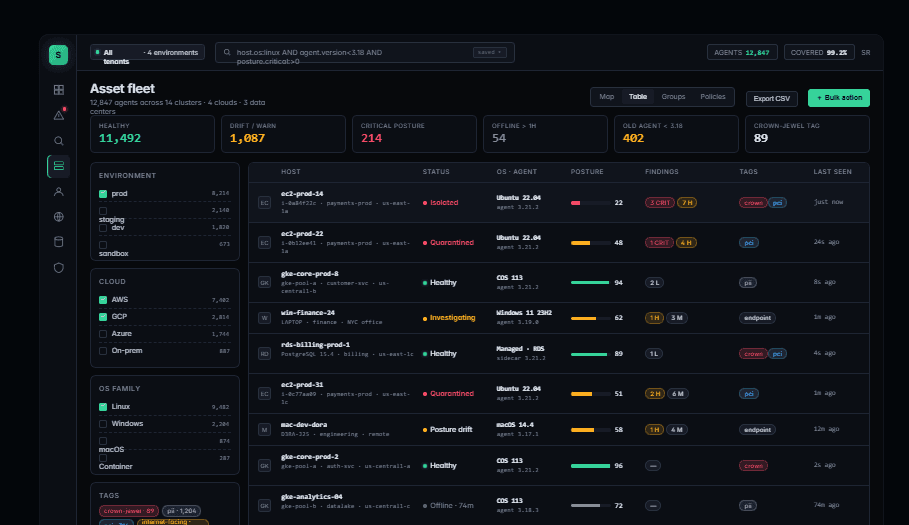
Cluster, region, and host-level health view. Detector coverage per asset, ingest lag, and false-positive trend per detection rule.
What changed for the team.
Have a similar AI project in mind?
We design and ship production-grade AI systems for UAE businesses — from focused MVPs to enterprise platforms. Free scoping call, written estimate within 5 business days.
Start a conversation →Project Gallery
On-site photo log
More Projects
Related Work
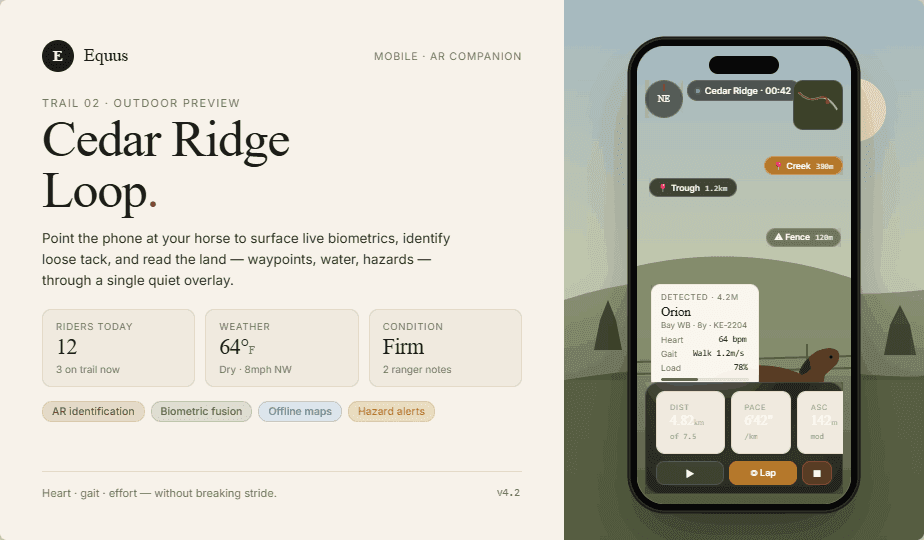
Equus — AR & AI Companion for Equestrian Training
An AI-powered AR companion for equestrian training. Riders point a phone at their horse to surface live biometrics, hazards, and waypoints; trainers manage horses, training load, and health from a unified web console. Built for stables and federations across the UAE.
View project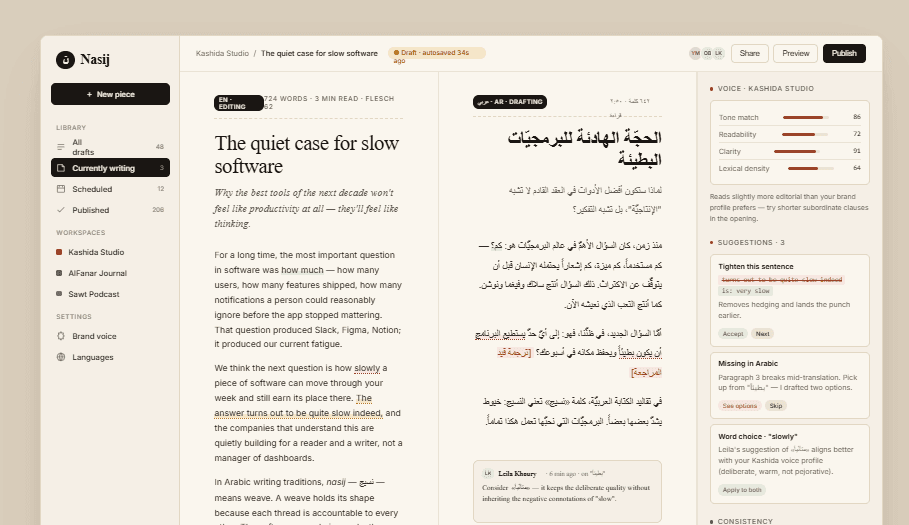
Nasij — AI Arabic Content Studio for Brand Voice
An AI-powered Arabic-English content studio that learns a brand's voice from twenty posts, then writes Khaleeji or Modern Standard Arabic with brand-correct tone, vocabulary, and cadence. Built for UAE marketing teams who can't ship Google-Translate Arabic.
View project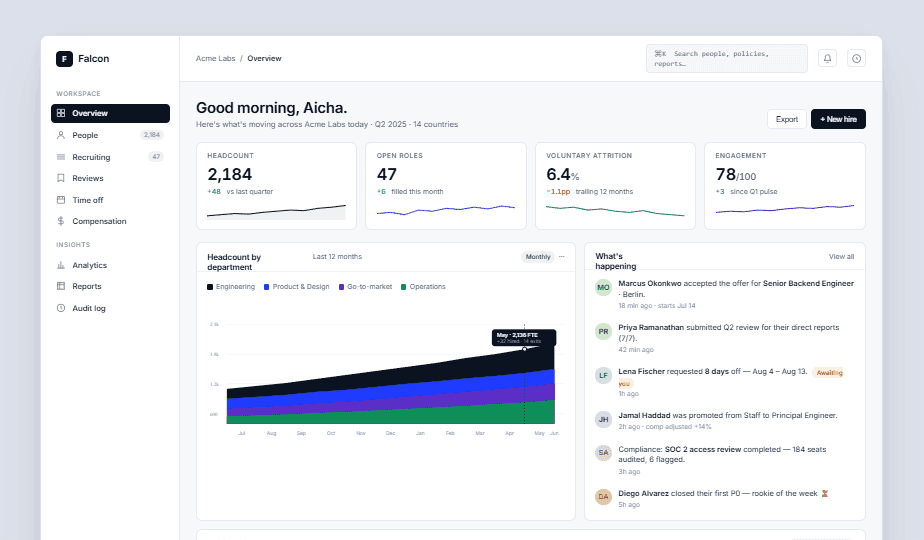
Falcon Vision — AI-Assisted People Operations Platform
An AI-augmented people-operations platform for fast-growing global tech employers. Combines headcount and engagement analytics, an applicant tracking kanban with AI candidate scoring, employee profile and compensation views, and audit-ready exports for finance and compliance.
View projectHave a Similar Project?
Let us help you bring your vision to life with a tailored technology solution.